
Cloud. Secure. Scale.
We architect, secure, and scale your AWS infrastructure with security-first expertise. Transform your cloud journey with confidence.
Cloud Excellence in Action
Experience how our cloud expertise transforms your infrastructure with automation, optimization, and security best practices.
Meet KloudSec
The same AWS security expertise we bring to consulting, now as a platform. Continuous scanning. Automated remediation. Zero noise.
API-first. Full CLI. IaC scanning for Terraform and CloudFormation. Application code SAST across 11 languages. Secrets detection across GitHub, EC2, Lambda, and ECS.
AWS Security & Architecture Experts
We don't do everything. We do AWS security and architecture exceptionally well. When you hire a generalist, security and architecture are afterthoughts. Here, they're the entire job.
AWS Security Consulting
Security assessments, IAM audits, compliance automation (HIPAA, GDPR, SOC2), GuardDuty & Security Hub implementation. We harden your AWS environment before attackers find the gaps.
Cloud Architecture
Resilient, secure-by-design AWS architectures. Multi-account landing zones, Well-Architected reviews, and cost-optimized infrastructure built to scale.
AWS Migration
Security-first cloud migrations. We move your workloads to AWS with zero-trust architecture, proper IAM design, and encryption enforced from day one.
The Toc Consulting Advantage
Our expertise, experience, and client-centered approach set us apart in the cloud consulting landscape.
Performance Optimization
We identify root causes of latency in your AWS stack - misconfigured services, wrong instance types, missing caching - and fix them.
- Measurable improvement in application performance
- Optimized resource allocation across services
- Reduced latency and improved user experience
Cost Efficiency
Overprovisioned instances, forgotten snapshots, idle NAT gateways - we find the waste. Our clients typically cut their AWS bill by 20-40% after a cost review.
- Significant reduction in cloud spending
- Detailed cost attribution and monitoring
- Predictable billing and budget management
Dedicated Expert Support
Responsive assistance from our team of certified cloud specialists.
- Fast, responsive expert support
- Dedicated support team for critical issues
- Proactive monitoring and issue prevention
Rapid Implementation
No 6-month onboarding. Assessment in week one, prioritized action plan in week two, implementation starting in week three.
- Accelerated project delivery with proven methodologies
- Streamlined migration process with minimal downtime
- Continuous integration and deployment capabilities
This Week in AWS Security
CVEs, service updates, breach analysis, threat intelligence. Curated weekly.
Six AWS Bulletins: A Neptune Flaw Rated 9.9 and a KVM Host-Memory Issue
Six new AWS security bulletins this week, led by an Amazon Neptune query-engine issue that its CVE record scores 9.9 (CRITICAL) and a Linux kernel virtio-net/TAP flaw that affects self-managed KVM hosts but not EC2, Lambda or Fargate. On the defensive side, OpenSearch Service gets per-index KMS keys, Security Hub adds resource criticality and the Cyber Risk Institute profile, Secrets Manager rotates Databricks and Twilio credentials, and Transfer Family host keys can live in Secrets Manager.
Eight AWS Bulletins, Including a Cross-Account Athena Authorization Gap
Eight new AWS security bulletins this week, led by a code injection in the deprecated Bedrock AgentCore Starter Toolkit and a now-fixed Athena engine version 3 authorization gap that could have exposed query metadata across accounts. On the defensive side, GuardDuty RDS Protection now watches database query activity for exfiltration and destruction, and IAM Identity Center can restrict where Identity Store and SCIM API calls come from.
A CVSS 10.0 in AWS Labs' Loom and a SageMaker Unified Studio Credential Exposure
Seven new AWS bulletins this week, led by a CVSS 10.0 authentication bypass in Loom, an AWS Labs agent orchestration platform, and a SageMaker Unified Studio flaw that, in projects with Trusted Identity Propagation enabled, could let a project contributor obtain another member's temporary role credentials. On the defensive side, Security Hub added remediation plans, GuardDuty can now be enforced through Organizations declarative policies, and CloudTrail now shows where data-event logging is missing.
AWS Security Cards
Attack vectors, misconfigurations, CLI commands, and detection indicators for 54 AWS services. One card per service. 100% free.
Featured cards:
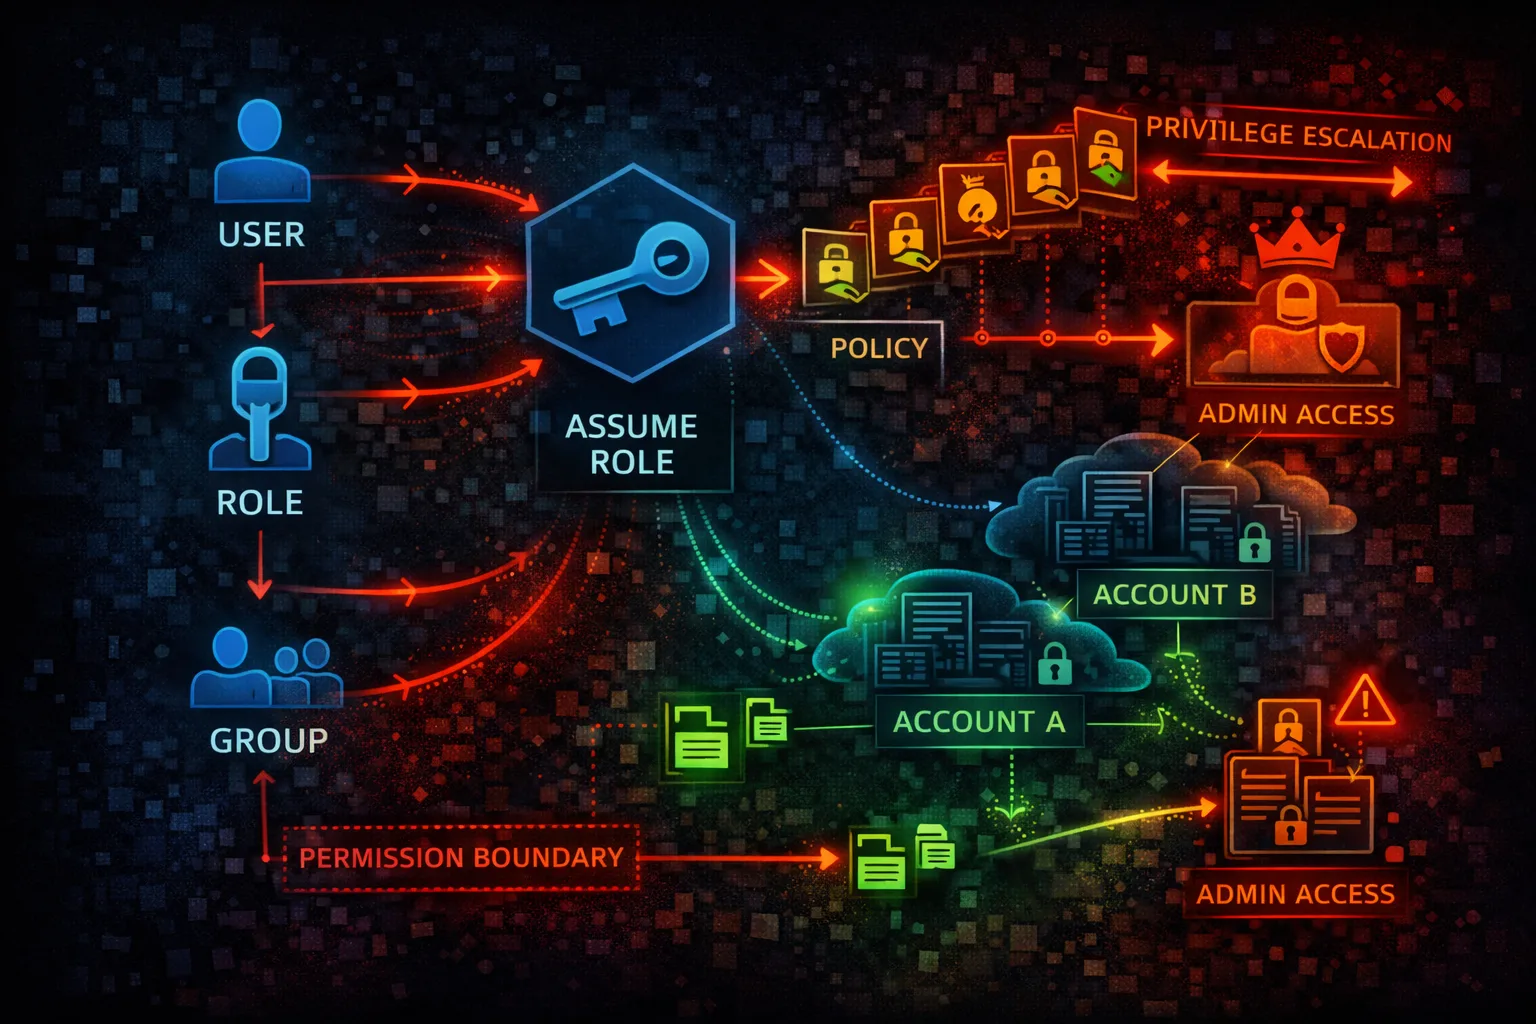
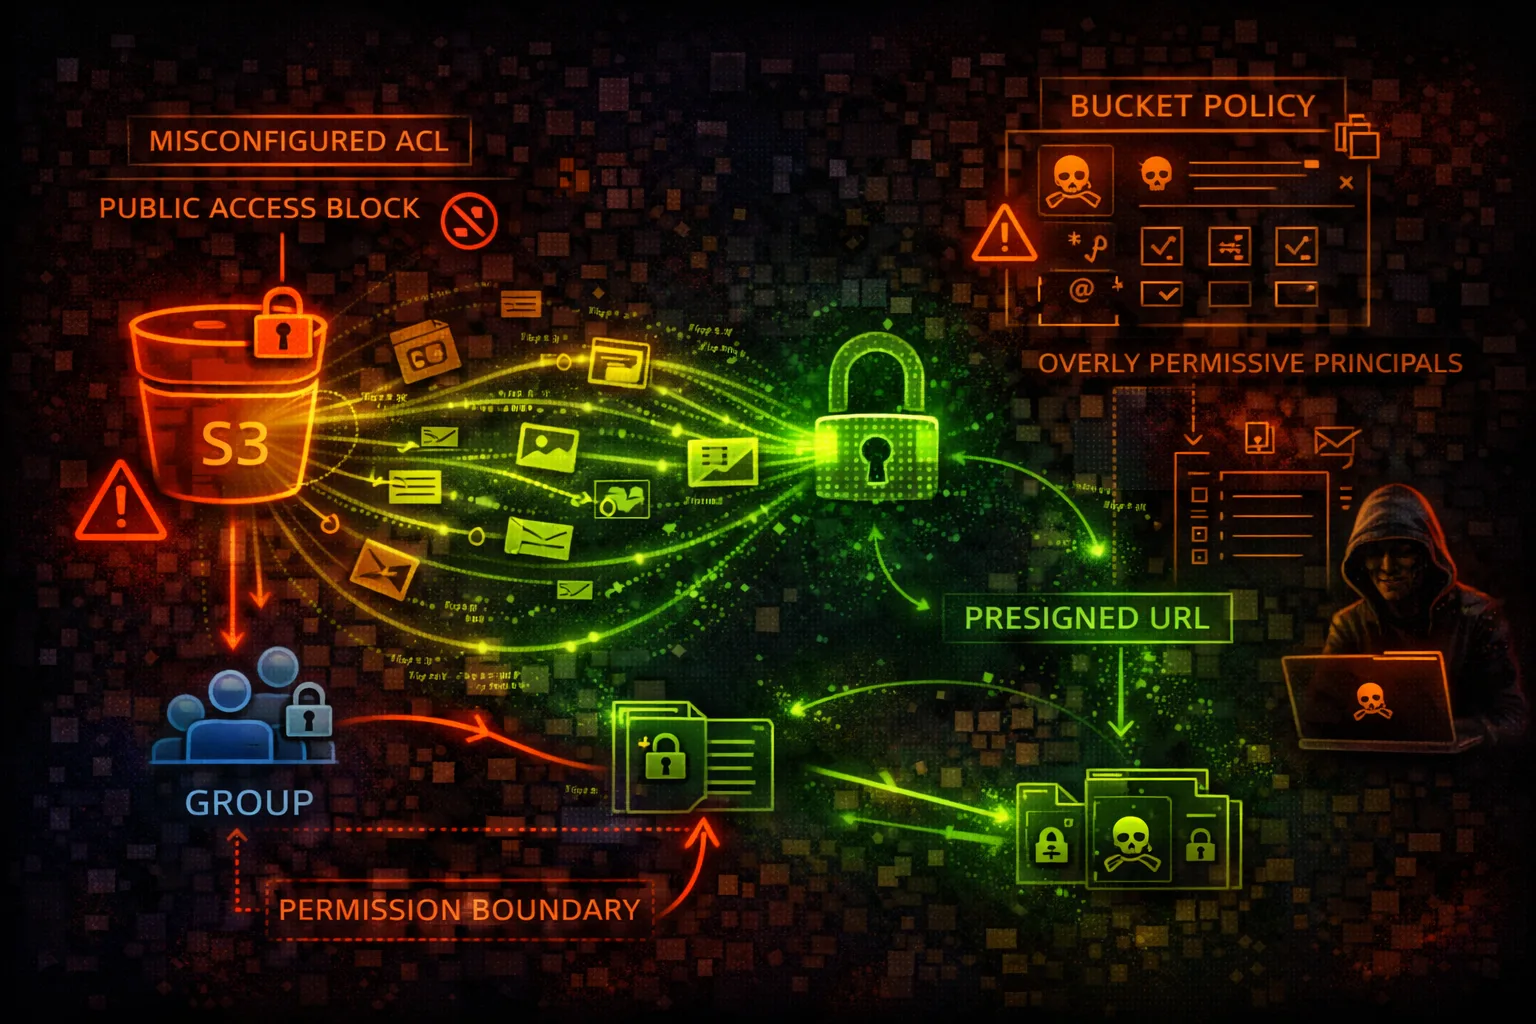
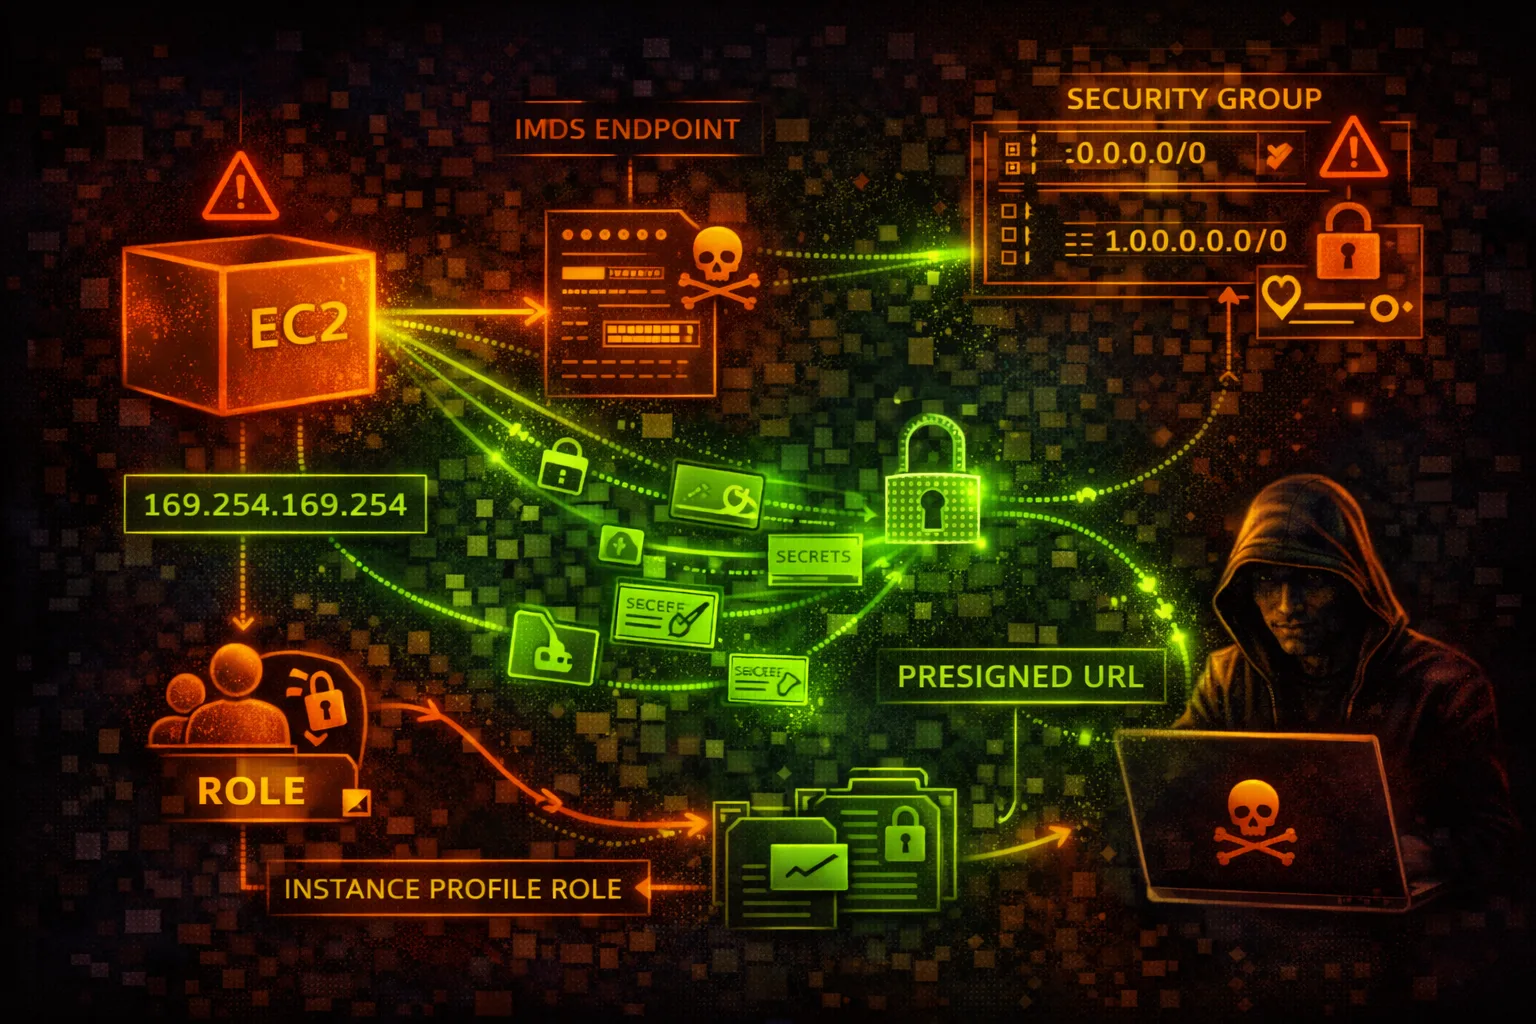
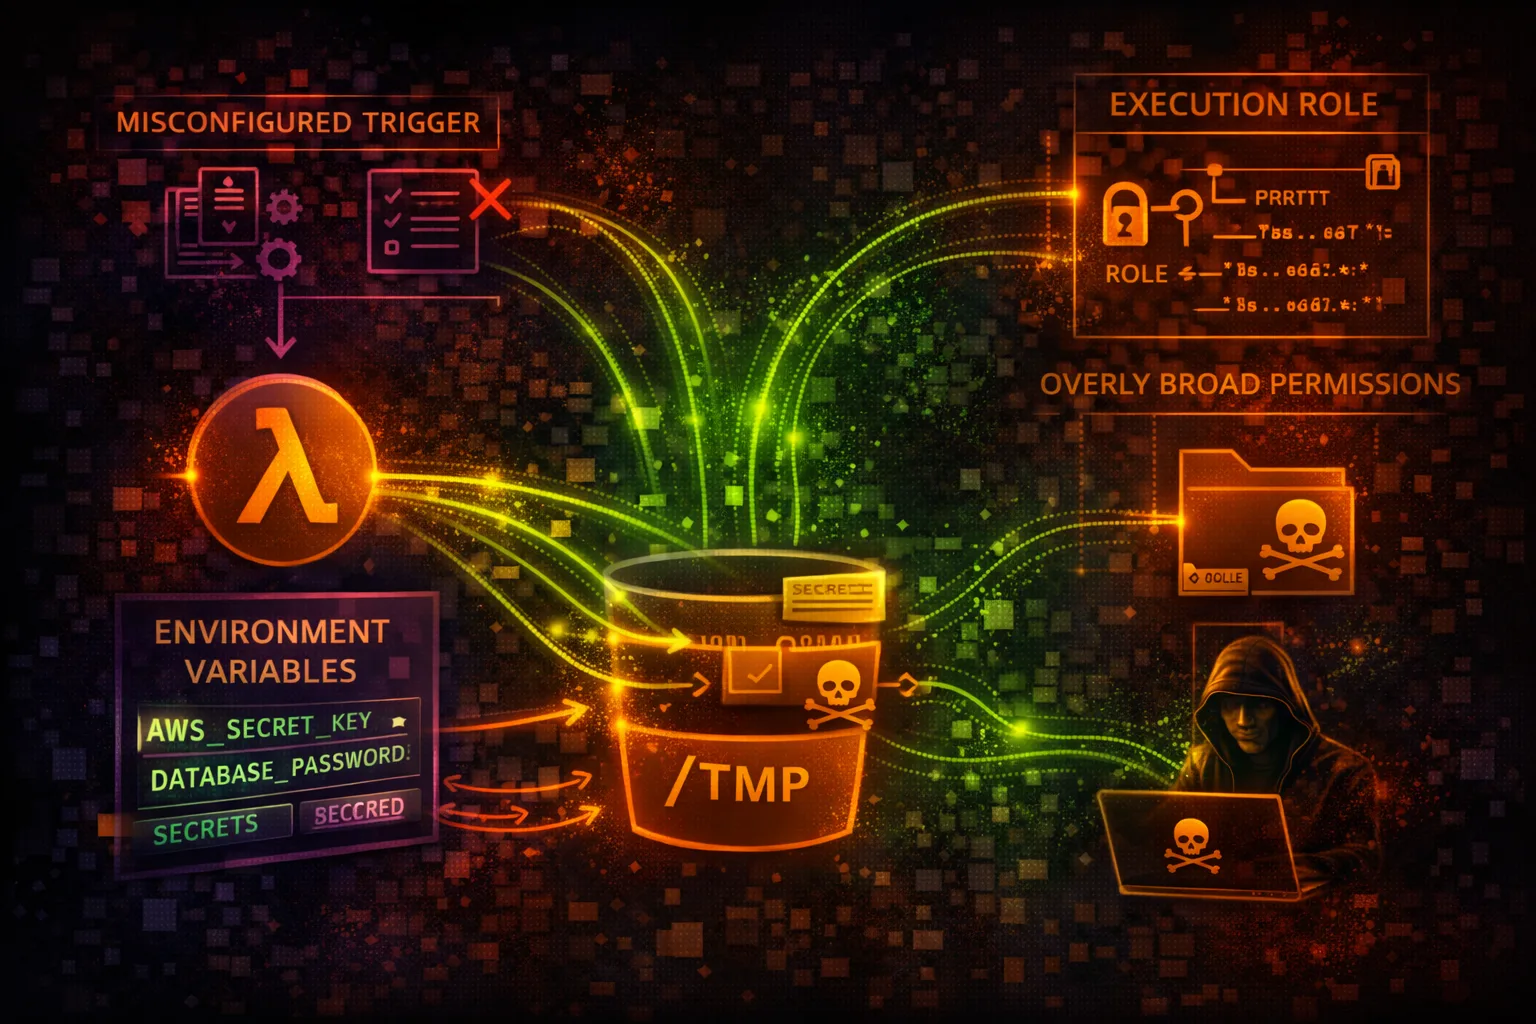
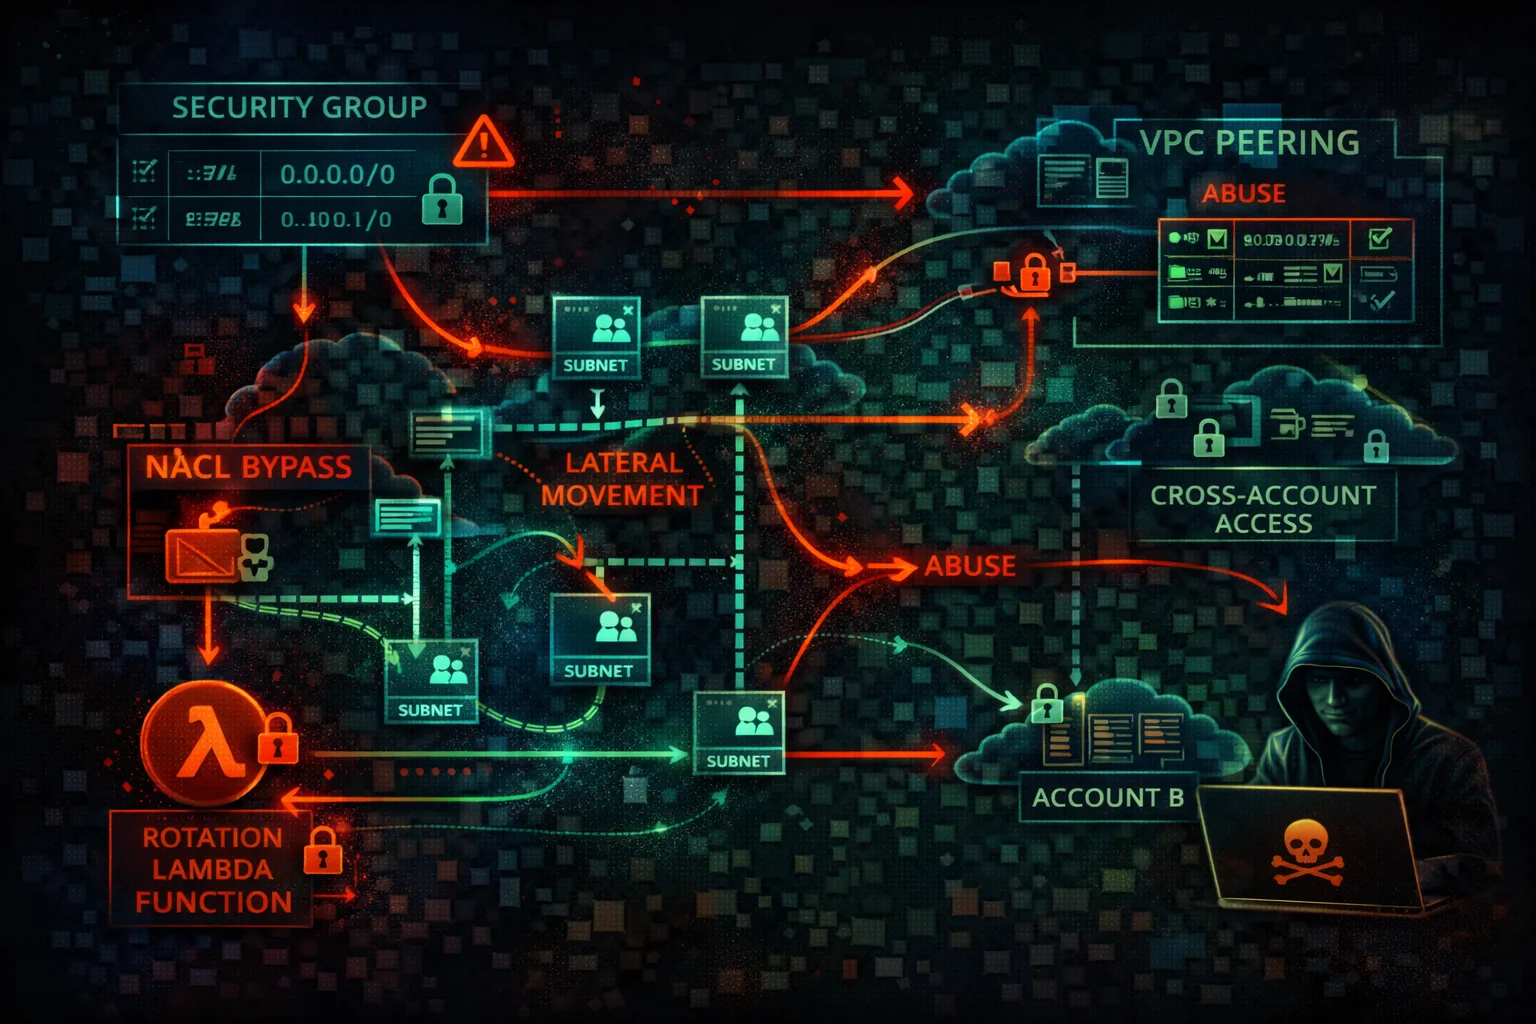
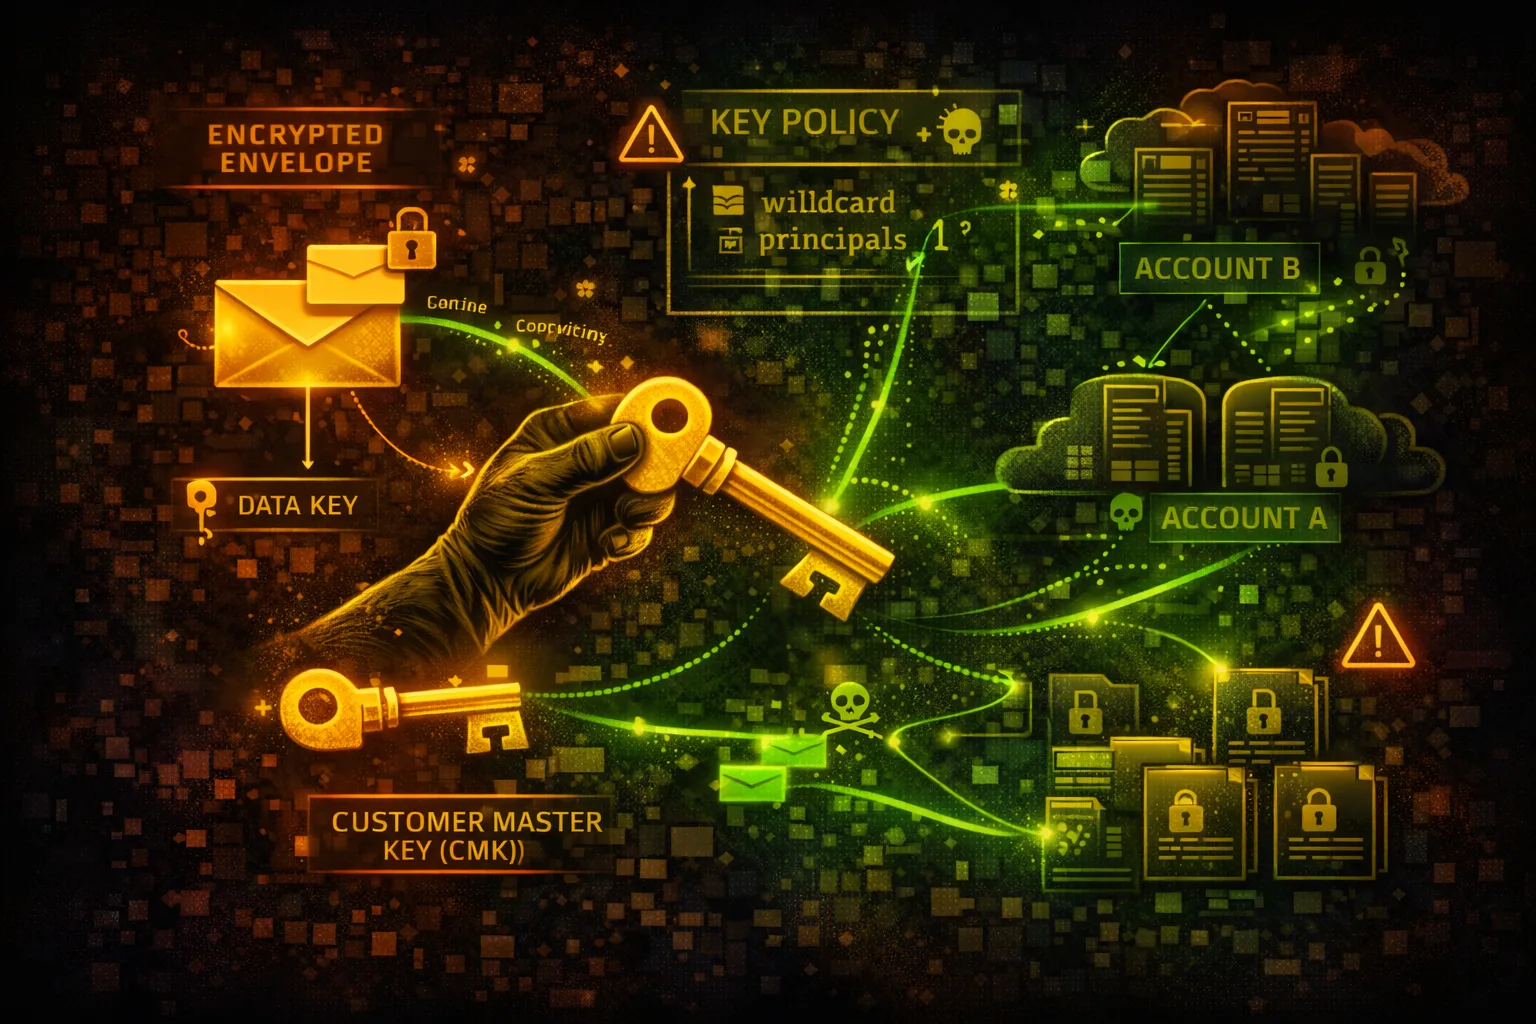
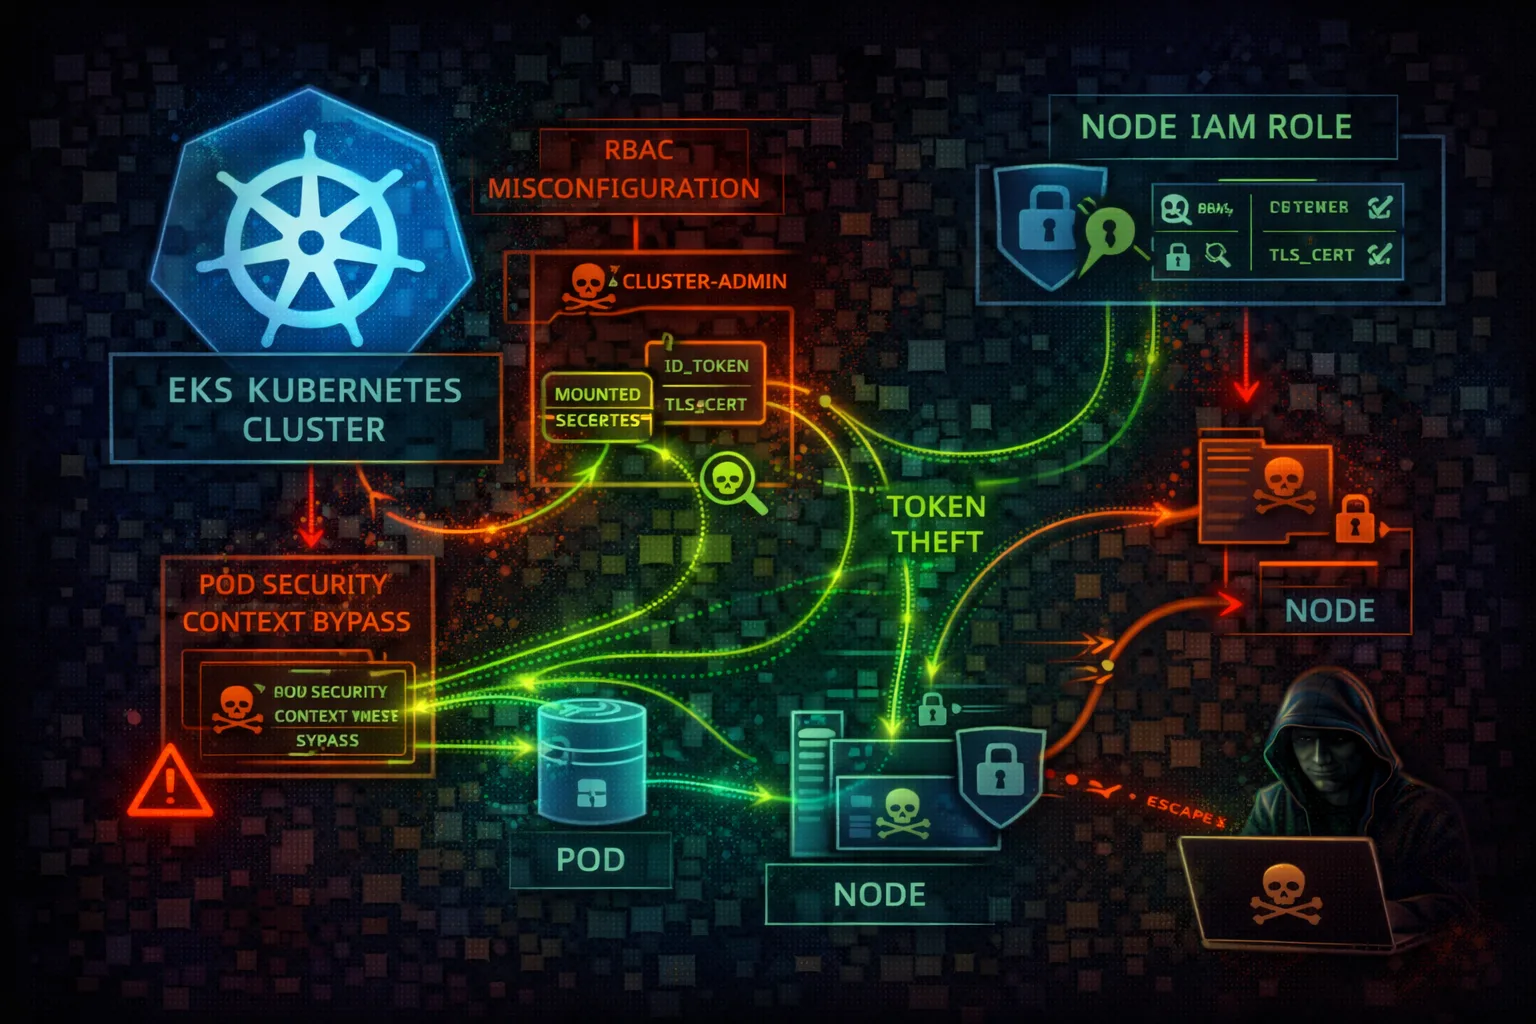
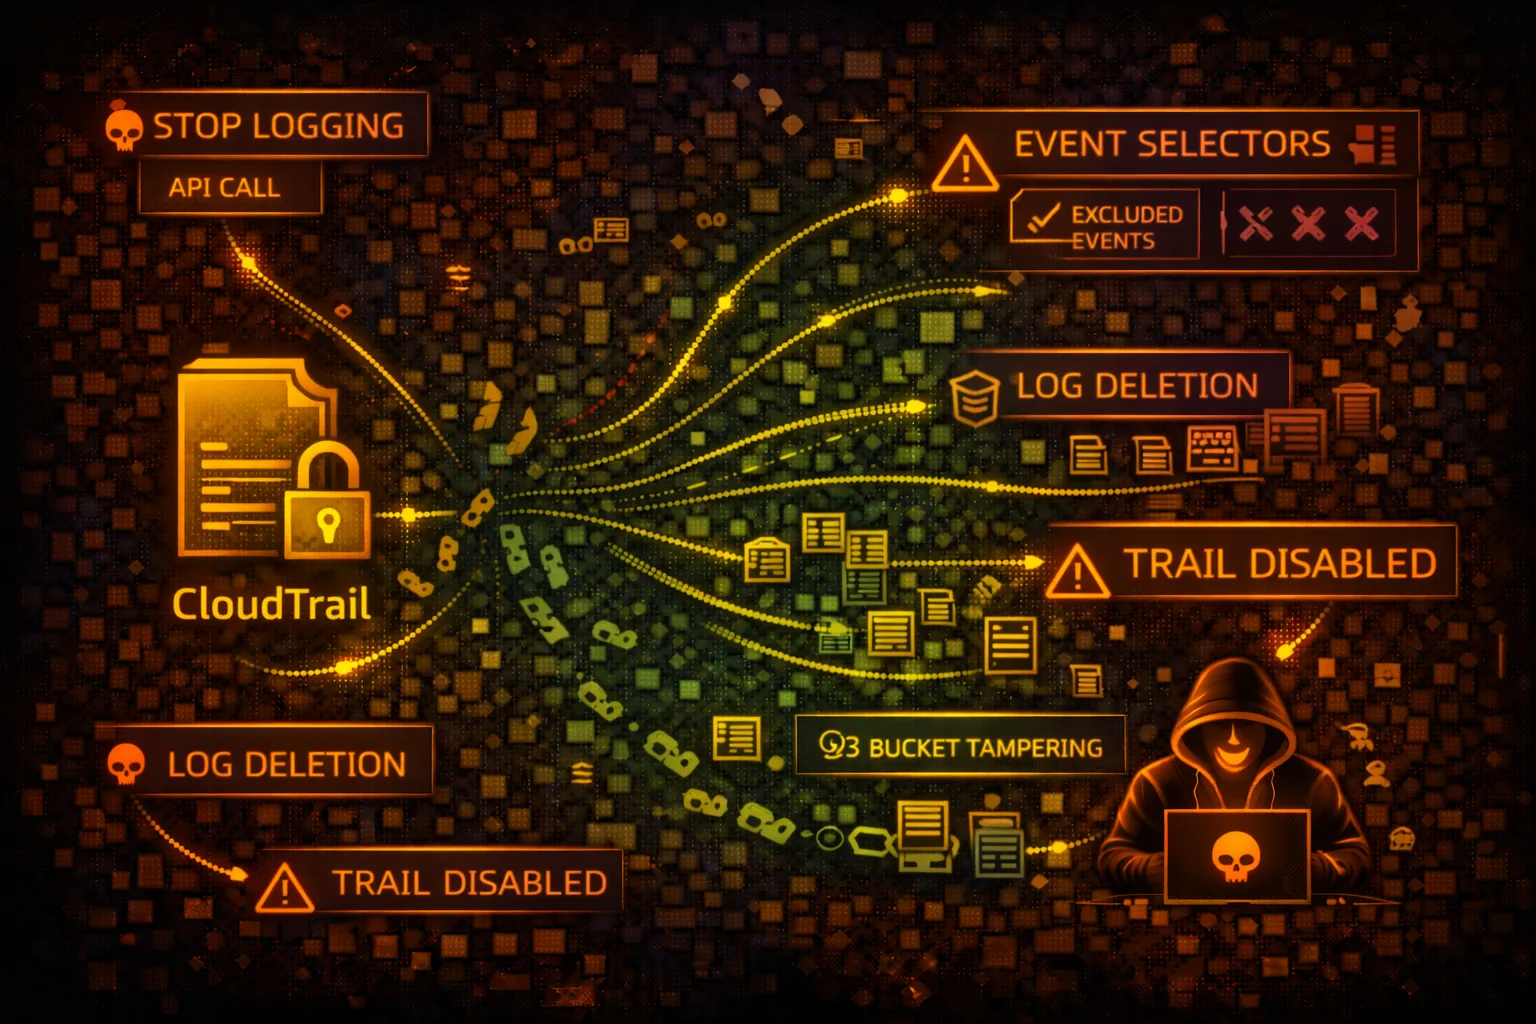
Covers IAM, S3, EC2, Lambda, EKS, RDS, DynamoDB, CloudFront, WAF, Bedrock, SageMaker, and 43 more
Experience Across Leading Organizations
We've worked directly inside the AWS infrastructure of major French enterprises and public institutions, not as account managers, but as hands-on engineers.
The State of AWS Security 2026
A practitioner's guide from IAM to Agentic AI. No fluff - just controls you can deploy today.
Toc Consulting
The State of AWS Security 2026
From IAM to Agentic AI: A Practitioner's Guide
By Tarek Cheikh
What's inside:
Ready to Transform Your Cloud Infrastructure?
Tell us what keeps you up at night: a looming audit, a security gap you can't close, or AWS bills that don't add up. We'll give you a straight answer.
Schedule Free Consultation